
Dülger Law Office/Publications/Book
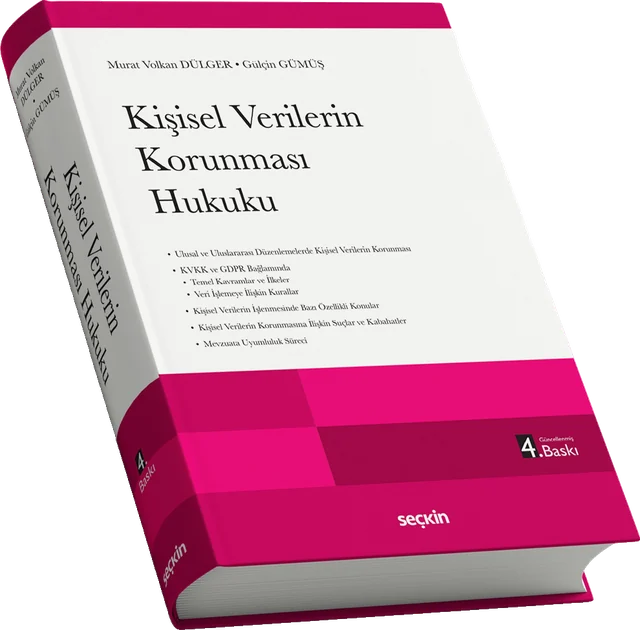
Personal Data Protection Law
(Kişisel Verilerin Korunması Hukuku)
About the book
This work was written in Turkish. The summary on this page is a translation; the citation gives the original title in parentheses.
When this book first took shape, the aim was to treat the field of personal data protection law as a whole and so to understand its essence. The same approach has been adopted in this edition, prepared after a long interval, and care has been taken to reflect in the book all the developments that have occurred in the meantime. In this context, the changes in legislation and recent court decisions have been worked into the book; debates that are no longer current have been removed or shortened to make room for new areas of debate that reflect the changing structure of personal data protection law.
In addition, the relationship between the right to the protection of personal data and human rights is treated as a basic point of reference in this edition, as it has been since the first edition of the book. The growing importance of personal data protection in the new way of life shaped by today’s technological developments is given particular emphasis throughout the book. The result is a work that reflects the stage reached in the field of personal data protection law. It is addressed both to undergraduate students interested in this field and to lawyers and consultants who carry on their professional activities in it.
Table of contents
Table of contents of the 4th edition (February 2026). The book is in Turkish; the headings below are a translation. Page numbers refer to the printed book. Select a chapter to see its sub-headings.
- Preface to the Fourth Edition6
- Preface to the Third Edition7
- Preface to the Second Edition9
- Preface to the First Edition11
- Abbreviations31
Chapter OneTHE CONCEPT OF PERSONAL DATA AND THE PROTECTION OF PERSONAL DATA AS A RIGHT72 headings
- § 1.THE CONCEPT OF PERSONAL DATA33
- I.DEFINITION OF PERSONAL DATA33
- II.SCOPE AND ELEMENTS OF PERSONAL DATA37
- A.In General37
- B.Elements of Personal Data38
- 1.Existence of a Piece of Data38
- 2.The Data Rendering the Person Identified or Identifiable43
- a.Direct Identifiers44
- b.Indirect Identifiers44
- c.Limits of Identifiability49
- d.The Status of Anonymised Data50
- e.The Status of Pseudonymised (Aliased / Masked / Redacted) Data51
- f.The Status of Encrypted or Partially Redacted Data53
- 3.The Data Relating to a Person53
- 4.The Data Belonging to a Natural Person56
- C.Data Giving Rise to Doubt as to Whether They Are Personal Data60
- 1.In General60
- 2.The Status of Unclassified Physical Data61
- III.SPECIAL CATEGORIES OF (SENSITIVE) PERSONAL DATA62
- § 2.EMERGENCE OF THE RIGHT TO THE PROTECTION OF PERSONAL DATA64
- I.IN GENERAL64
- II.PERSONAL DATA AND THE SURVEILLANCE SOCIETY65
- A.Surveillance in Modern Society66
- 1.The Conception of Surveillance of Karl Marx, Max Weber and George Orwell69
- 2.Michel Foucault’s Conception of Surveillance72
- B.Electronic Surveillance Emerging as a Result of Technological Developments74
- III.NATURE OF THE RIGHT TO THE PROTECTION OF PERSONAL DATA74
- A.In General74
- B.Legal Nature of the Right to the Protection of Personal Data75
- 1.The View That It Is an Economic Right76
- a.The View That It Is a Property Right76
- b.The View That It Is an Intellectual Property Right78
- 2.The View That It Is a Human Right78
- C.The Debate on Whether It Is an Independent Right79
- 1.The View That Considers It under the Right to Respect for Private Life79
- 2.The View That It Is an Independent Right80
- 3.Our View81
- § 3.PROTECTION OF PERSONAL DATA IN THE FUNDAMENTAL INSTRUMENTS85
- I.PROTECTION OF PERSONAL DATA IN INTERNATIONAL INSTRUMENTS85
- A.OECD (Organisation for Economic Co-operation and Development)85
- B.United Nations87
- 1.Universal Declaration of Human Rights87
- 2.United Nations International Covenant on Civil and Political Rights (ICCPR)87
- 3.UN Guidelines for the Regulation of Computerized Personal Data Files89
- C.Council of Europe89
- 1.Convention No. 108 for the Protection of Individuals with regard to Automatic Processing of Personal Data90
- 2.Additional Protocol to the Convention for the Protection of Individuals with regard to Automatic Processing of Personal Data, regarding Supervisory Authorities and Transborder Data Flows (Protocol on Transborder Data Flows)92
- 3.European Convention on Human Rights93
- D.The European Union94
- 1.Directive 95/46/EC of the European Parliament and of the Council on the Protection of Individuals with regard to the Processing of Personal Data and on the Free Movement of Such Data (Data Protection Directive)95
- 2.Charter of Fundamental Rights of the European Union99
- 3.Directive 2002/58/EC of the European Parliament and of the Council concerning the Processing of Personal Data and the Protection of Privacy in the Electronic Communications Sector (ePrivacy Directive)100
- 4.Directive 2016/680 on the Protection of Personal Data in Law Enforcement and Criminal Proceedings (Law Enforcement Directive – LED)100
- 5.Regulation (EU) 2018/1725 on Data Protection by the Institutions of the European Union102
- 6.European Union General Data Protection Regulation 2016/679 (GDPR)102
- II.PROTECTION OF PERSONAL DATA IN NATIONAL LEGISLATION110
- A.The 1982 Constitution110
- B.Law on the Protection of Personal Data112
- C.Turkish Criminal Code113
- § 4.PROTECTION OF PERSONAL DATA AS A HUMAN RIGHT113
- I.THE CONCEPT OF A HUMAN RIGHT113
- II.THE PLACE OF THE RIGHT TO THE PROTECTION OF PERSONAL DATA AMONG HUMAN RIGHTS116
- III.THE RIGHT TO THE PROTECTION OF PERSONAL DATA IN THE JUDGMENTS OF THE EUROPEAN COURT OF HUMAN RIGHTS118
- A.Scope of the Concept of Private Life Referred to in Article 8 of the Convention119
- B.The Requirement That Interference with the Right to the Protection of Personal Data Be Based on a Statutory Provision130
- C.Unlawful Storage, Use and Disclosure of Personal Data134
- D.The Requirement That Interferences with the Right to the Protection of Personal Data Be Limited to a Legitimate Aim135
- IV.THE RIGHT TO THE PROTECTION OF PERSONAL DATA IN THE JUDGMENTS OF THE CONSTITUTIONAL COURT139
- A.Scope of the Concept of Private Life Referred to in Article 20 of the Constitution139
- B.The Right to the Protection of Personal Data Protected by Paragraph 3 of Article 20 of the Constitution and Its Scope142
- C.The Requirement That the Right to the Protection of Personal Data Be Regulated by Law144
- V.ASSESSMENT AND OUR VIEW146
Chapter TwoSCOPE AND CONTENT OF THE LAW, BASIC CONCEPTS AND PRINCIPLES86 headings
- § 5.THE NEED TO PROTECT PERSONAL DATA THROUGH A BASIC PIECE OF LEGISLATION, AND THE DEVELOPMENT AND EMERGENCE OF THE LEGISLATION151
- I.THE NEED TO PROTECT PERSONAL DATA THROUGH LEGISLATION151
- II.DEVELOPMENT AND EMERGENCE OF THE LEGISLATION161
- § 6.THE DATA PROTECTION SYSTEM PROVIDED FOR BY THE LAW164
- I.IN GENERAL164
- II.SCOPE AND STRUCTURE OF THE LAW ON THE PROTECTION OF PERSONAL DATA (KVKK)167
- A.Purpose167
- B.Scope169
- 1.Cases Falling within the Scope of the Law169
- a.Natural Persons Whose Personal Data Are Processed169
- b.Natural and Legal Persons Who Process Personal Data170
- c.Processing of Personal Data Wholly or Partly by Automated Means or, Provided That It Forms Part of a Data Filing System, by Non-Automated Means170
- 2.Cases Falling outside the Scope172
- a.Cases Wholly Excluded from the Scope of the Law172
- i.Processing of Personal Data by Natural Persons in the Course of Activities Relating Exclusively to Themselves or to Family Members Living in the Same Dwelling, Provided That the Data Are Not Disclosed to Third Parties and the Obligations Relating to Data Security Are Complied With172
- ii.Processing of Personal Data for Official Statistics and, by Being Anonymised, for Purposes Such as Research, Planning and Statistics174
- iii.Processing of Personal Data for Artistic, Historical, Literary or Scientific Purposes or within the Scope of Freedom of Expression175
- iv.Processing of Personal Data within the Scope of Preventive, Protective and Intelligence Activities Carried Out by Public Institutions and Organisations Assigned Duties and Powers by Law to Safeguard National Defence, National Security, Public Security, Public Order or Economic Security177
- v.Processing of Personal Data by Judicial Authorities or Execution Authorities in Connection with Investigation, Prosecution, Trial or Execution Proceedings179
- b.Cases Partly Excluded from the Scope of the Law181
- i.In General181
- ii.Where the Processing of Personal Data Is Necessary for the Prevention of Offences or for a Criminal Investigation182
- iii.Processing of Personal Data Made Public by the Data Subject Himself or Herself183
- iv.Where the Processing of Personal Data Is Necessary for the Performance of Supervisory or Regulatory Duties and for Disciplinary Investigation or Prosecution by Competent and Authorised Public Institutions and Organisations and by Professional Organisations with the Status of Public Institutions, on the Basis of Authority Conferred by Law184
- v.Where the Processing of Personal Data Is Necessary for the Protection of the Economic and Financial Interests of the State in Budgetary, Tax and Fiscal Matters184
- C.Basic Principles Relating to the Processing of Personal Data in the KVKK184
- III.THE SUPERVISORY MECHANISM PROVIDED FOR IN THE KVKK186
- IV.THE PERSONAL DATA PROTECTION AUTHORITY, ITS ORGANISATIONAL STRUCTURE AND DUTIES189
- A.In General189
- B.The Personal Data Protection Board and Its Duties190
- C.The Presidency192
- V.RELEVANT REGULATIONS192
- VI.DECISIONS OF THE BOARD193
- § 7.BASIC CONCEPTS RELATING TO THE PROTECTION OF PERSONAL DATA195
- I.IN GENERAL195
- II.BASIC CONCEPTS195
- A.Processing of Personal Data195
- B.Data Filing System197
- C.Data Subject200
- D.Controller201
- E.Joint Controller210
- 1.The Concept210
- 2.The Place of the Joint Controller in the KVKK and the GDPR211
- 3.Judgment of the Court of Justice of the European Union (CJEU) of 5 June 2018 in Wirtschaftsakademie and Facebook Ireland216
- 4.Judgment of the CJEU of 10 July 2018 in Jehovah’s Witnesses219
- 5.Judgment of the CJEU of 29 July 2019 in Fashion ID and Facebook Ireland222
- F.Processor224
- 1.In General224
- 2.The Processor in the GDPR230
- a.Obligations of the Processor230
- b.The Contract to Be Concluded between the Processor and the Controller232
- G.Explicit Consent234
- H.Transfer of Personal Data238
- I.Data Controllers’ Registry239
- İ.Personal Data Breach240
- J.Erasure, Destruction or Anonymisation of Personal Data243
- § 8.PRINCIPLES OF DATA PROTECTION LAW245
- I.IN GENERAL245
- II.BASIC PRINCIPLES RELATING TO THE PROCESSING OF PERSONAL DATA246
- A.Fairness and Compliance with the Rule of Good Faith247
- 1.Compliance with the Law and the Rules of Good Faith under the KVKK247
- 2.Lawfulness, Fairness and Transparency under the GDPR255
- B.Processing for Specified, Explicit and Legitimate Purposes258
- 1.Collection of Data for Specified, Explicit and Legitimate Purposes259
- a.The Purpose Being Specified and Explicit259
- b.The Purpose Being Legitimate262
- 2.Processing of Data in Accordance with the Purposes Specified for Their Collection265
- C.Data Being Relevant, Limited and Proportionate to the Purpose for Which They Are Processed268
- 1.Personal Data Must Be Relevant to the Purpose of Processing270
- 2.Purpose Limitation270
- 3.The Amount of Data Must Be Limited/Proportionate to What Is Necessary for the Purpose Determined by the Controller271
- a.Importance and Understanding of the Principle271
- b.Other Points to Be Noted with a View to Compliance with the Principle280
- D.Being Accurate and, Where Necessary, Kept up to Date281
- 1.In General281
- 2.The Status of Inaccurately Processed Data285
- 3.When Data Must Be Kept up to Date286
- 4.Responsibilities of the Controller and the Data Subject in Obtaining Up-to-Date Information286
- E.Retention of Data for the Period Necessary for the Purpose290
- 1.In General290
- 2.Cases in Which Personal Data Have Become Unnecessary or Purposeless for the Intended Purpose291
- 3.The Period Determined by the Controller for the Purpose of Data Processing292
- 4.Choosing One of the Methods of Erasure, Destruction or Anonymisation in Order to Eliminate Personal Data That Have Become Unnecessary or Purposeless for the Intended Purpose293
- F.Integrity and Confidentiality295
- G.The Accountability Requirement296
- H.Data Protection by Design and by Default298
Chapter ThreeRULES ON DATA PROCESSING IN PERSONAL DATA PROTECTION LAW137 headings
- § 9.CONDITIONS FOR THE PROCESSING OF PERSONAL DATA301
- I.IN GENERAL301
- II.PROCESSING OF PERSONAL DATA302
- A.Conditions for the Processing of Personal Data Other than Special Categories304
- 1.Explicit Consent of the Data Subject306
- a.Conditions of Explicit Consent307
- i.Relating to a Specific Matter307
- ii.Being Informed309
- iii.Being Expressed of One’s Own Free Will311
- b.Additional Conditions Relating to Consent in the GDPR313
- c.The Problem of Consent in the Processing of Children’s Personal Data315
- i.In General315
- ii.Consent of the Holder of Parental Responsibility316
- iii.The Requirement That Consent Be Informed317
- iv.The Approach of the Personal Data Protection Authority317
- d.Controversial Points Relating to Explicit Consent318
- i.Comparison of Explicit Consent and the Statutory Conditions for the Processing of Personal Data318
- ii.Obtaining Explicit Consent despite the Existence of the Processing Conditions Listed in the Law318
- iii.Whether Explicit Consent May Be Made Subject to a Condition320
- iv.Providing Additional Advantages in Return for Consent When Obtaining Explicit Consent323
- v.The Manner of Obtaining Explicit Consent326
- vi.Whether Explicit Consent May Be Withdrawn328
- vii.Validity of Data Obtained with Lawful Consent before the Date of Entry into Force of the KVKK329
- 2.Being Expressly Provided for in Laws332
- 3.Where It Is Necessary for the Protection of the Life or Physical Integrity of a Person Who Is Unable to Express Consent Owing to Actual Impossibility or Whose Consent Is Not Recognised as Legally Valid, or of Another Person335
- 4.Where the Processing of Personal Data of the Parties to a Contract Is Necessary, Provided That It Is Directly Related to the Conclusion or Performance of the Contract337
- 5.Where It Is Necessary for the Controller to Fulfil Its Legal Obligation343
- 6.Where the Data Have Been Made Public by the Data Subject Himself or Herself346
- 7.Where Data Processing Is Necessary for the Establishment, Exercise or Protection of a Right355
- 8.Where Data Processing Is Necessary for the Legitimate Interests of the Controller, Provided That the Fundamental Rights and Freedoms of the Data Subject Are Not Harmed357
- B.Conditions for the Processing of Special Categories of Personal Data362
- 1.In General362
- 2.Certain Debates Concerning the Scope of Special Categories of Personal Data363
- 2.Explicit Consent369
- 3.Being Expressly Provided for in Laws370
- 4.Where It Is Necessary for the Protection of the Life and Physical Integrity of a Person Who Is Unable to Express Consent Owing to Actual Impossibility or Whose Consent Is Not Recognised as Legally Valid, or of Another Person371
- 5.In the Case of Personal Data Made Public by the Data Subject, Conformity with the Data Subject’s Intention in Making Them Public371
- 6.Where It Is Necessary for the Establishment, Exercise or Protection of a Right373
- 7.Where It Is Necessary for the Purposes of Protecting Public Health, Preventive Medicine, Medical Diagnosis, the Provision of Treatment and Care Services, and the Planning, Management and Financing of Health Services, by Persons under an Obligation of Secrecy or by Authorised Institutions and Organisations373
- 8.Where It Is Necessary for the Fulfilment of Legal Obligations in the Fields of Employment, Occupational Health and Safety, Social Security, Social Services and Social Assistance374
- 9.Where Processing by Foundations, Associations and Other Non-Profit Organisations or Bodies Established for Political, Philosophical, Religious or Trade-Union Purposes Concerns Their Current or Former Members and Affiliates or Persons in Regular Contact with Such Organisations and Bodies, Provided That It Complies with the Legislation to Which They Are Subject and with Their Purposes, Is Limited to Their Fields of Activity and the Data Are Not Disclosed to Third Parties375
- III.TRANSFER OF PERSONAL DATA376
- A.Transfer of Personal Data within the Country376
- B.Transfer of Personal Data Abroad382
- 1.In General382
- 2.Cases Deemed to Be Transfer Abroad383
- a.Transfer of Personal Data to a Foreign Country384
- b.The Status of Cloud Services384
- c.Transfer to a Company Whose Servers Are Located Abroad386
- 3.Conditions for Transfer Abroad386
- a.Transfer of Data Abroad Where an Adequacy Decision Exists388
- b.Transfer of Data Abroad in the Absence of an Adequacy Decision391
- i.Existence of an Agreement Not Having the Nature of an International Treaty392
- ii.Signing of a Standard Contract394
- iii.Binding Corporate Rules397
- iv.Signing of a Written Undertaking398
- c.Exceptional Transfer of Data Abroad Where There Is No Adequacy Decision and Appropriate Safeguards Cannot Be Provided Either398
- 4.Steps to Be Taken in Order by Controllers When Transferring Data Abroad400
- § 10.RIGHTS OF THE DATA SUBJECT402
- I.IN GENERAL402
- II.RIGHTS OF THE DATA SUBJECT403
- A.Transparent Information to the Data Subject on the Exercise of His or Her Rights403
- B.The Data Subject’s Right of Access407
- 1.Nature and Purpose of the Right407
- 2.Scope409
- C.Data Portability415
- D.Right to Rectification418
- E.Right to Object419
- F.Right to Erasure/Right to Be Forgotten422
- 1.The Process by Which the Right Emerged424
- 2.Scope433
- a.Where the Personal Data Are No Longer Necessary in Relation to the Purposes for Which They Were Collected or Processed435
- b.Where the Data Subject Objects to the Processing and There Are No Overriding Legitimate Grounds for the Processing436
- c.Where the Personal Data Have Been Unlawfully Processed437
- d.Where the Personal Data Must Be Erased in Order to Comply with a Legal Obligation to Which the Controller Is Subject437
- e.Where the Personal Data Concerned Were Collected in Connection with the Provision on Online Services Offered to Children439
- G.Right to Restriction of Processing440
- H.Right to Request That Third Parties Be Notified of the Operations441
- I.Right to Restrict Automated Decision-Making442
- İ.Right to Claim Compensation for Damage445
- III.MATTERS TO BE OBSERVED IN GIVING EFFECT TO THE RIGHTS OF THE DATA SUBJECT445
- A.As Regards the Procedure for Exercising the Rights445
- B.As Regards Time Limits449
- C.Fee453
- D.Verifying the Identity of the Persons Making a Request455
- E.Method to Be Used in Responding456
- IV.EXCEPTIONS459
- § 11.OBLIGATIONS OF THE CONTROLLER AND THE PROCESSOR460
- I.OBLIGATIONS OF THE CONTROLLER460
- A.Obligation to Inform460
- 1.In General460
- 2.Procedures and Principles to Be Followed in Fulfilling the Obligation to Inform461
- a.Scope of the Obligation to Inform461
- b.Procedures and Principles Relating to the Obligation to Inform462
- c.The Obligation to Inform Where the Personal Data Are Not Obtained from the Data Subject471
- B.Obligation to Enable the Data Subject to Exercise His or Her Rights472
- C.Obligations Relating to Data Security472
- 1.In General472
- 2.Decisions of the Board Relating to Data Security477
- a.Adequate Measures to Be Taken in Respect of Special Categories of Personal Data477
- i.Measures Relating to the Policy and Procedure for the Protection, Storage and Processing of Personal Data477
- ii.Measures Relating to Employees Involved in the Processing of Special Categories of Personal Data478
- iii.Where the Environments in Which Special Categories of Personal Data Are Processed, Stored and/or Accessed Are Electronic479
- iv.Where the Environments in Which Special Categories of Personal Data Are Processed, Stored and/or Accessed Are Physical481
- v.Transfer of Special Categories of Personal Data482
- vi.The Need to Take into Account, in Addition to the Measures Mentioned, the Technical and Administrative Measures for Ensuring an Appropriate Level of Security Set Out in the Personal Data Security Guide Published on the Website of the Personal Data Protection Board483
- vii.Other Measures, beyond the Minimum Level, to Be Taken by the Controller in View of the Purpose of Processing483
- b.Data Breach Notification486
- i.The Statutory Provisions and the Importance of the Subject486
- ii.Who Is to Make the Data Breach Notification?488
- iii.Time Limit for the Data Breach Notification488
- iv.Points to Be Noted in the Data Breach Notification490
- v.Failure to Make the Breach Notification at All or in the Proper Manner492
- c.Failure to Take the Necessary Administrative and Technical Measures for Ensuring an Appropriate Level of Security in Order to Safeguard Personal Data Security494
- D.Obligation to Register with the Data Controllers’ Registry500
- 1.In General500
- 2.Exceptions to the Registration Obligation501
- a.Exceptions Determined by Regulation501
- b.Exceptions Determined by Decisions of the Board502
- E.Erasure, Destruction or Anonymisation of Personal Data504
- 1.In General504
- 2.Methods and Measures Relating to Data Disposal505
- a.Personal Data Retention and Disposal Policy505
- b.Recording of Erasure, Destruction and Anonymisation and Retention of Those Records506
- c.Method of Erasure, Destruction and Anonymisation507
- d.Operations in Erasure, Destruction and Anonymisation508
- e.Taking out of Use Data That Cannot Be Disposed of for Technical Reasons513
- f.Time Limits for Ex Officio Erasure, Destruction and Anonymisation515
- g.Time Limits for Erasure and Destruction upon Request515
- 3.Disposal of Personal Data in Outline516
- II.OBLIGATIONS OF THE PROCESSOR519
- A.Nature of the Processor520
- B.Obligations of the Processor522
- C.Principles to Be Observed by Virtue of the Relationship between the Controller and the Processor524
- 1.As Regards the Selection of the Processor524
- 2.As Regards the Continuation of the Guarantees Provided by the Selected Processor524
- 3.The Principle of a Written Contract525
Chapter FourCERTAIN SPECIAL ISSUES IN THE PROCESSING OF PERSONAL DATA40 headings
- § 12.PROCESSING OF PERSONAL DATA IN THE EMPLOYEE–EMPLOYER RELATIONSHIP527
- I.PROCESSING OF PERSONAL DATA IN RECRUITMENT PROCESSES527
- A.Information and Documents That May Be Requested in the Recruitment Process528
- B.Sharing of Personal Data Obtained in Recruitment Processes529
- C.Continued Processing of Data after an Unsuccessful Job Application530
- II.PROCESSING OF PERSONAL DATA BY MEANS OF ELECTRONIC MONITORING AFTER THE ESTABLISHMENT OF THE EMPLOYMENT RELATIONSHIP532
- A.The Concept of Electronic Surveillance and Electronic Monitoring Practices Applied in the Workplace532
- 1.In General532
- 2.Reasons for Employers’ Recourse to Electronic Monitoring Practices534
- B.Processing of Personal Data by Means of Electronic Monitoring537
- 1.The Employer’s Power to Monitor the Employee537
- a.The Power to Monitor in General and Its Limits537
- b.Monitoring of Employees’ Work Computers, E-mails and WhatsApp Correspondence543
- i.Whether the Employee May Use Means of Communication for Private Purposes543
- i.Monitoring of Work Computers547
- ii.Monitoring of Employees’ Use of E-mail548
- iii.Monitoring of Employees’ WhatsApp Correspondence552
- c.Monitoring of Employees’ Entry to and Exit from the Workplace554
- d.Monitoring of Employees by Security Camera555
- 2.Whether Data Obtained by the Employer through Electronic Monitoring May Constitute a Valid Ground for Termination558
- C.Summary of the Subject in Outline and Our Assessments561
- III.PROTECTION OF PERSONAL DATA AFTER THE TERMINATION OF THE EMPLOYMENT RELATIONSHIP565
- A.Documents Submitted in an Action for Reinstatement565
- B.Continued Processing of a Former Employee’s Data568
- § 13.PROCESSING OF PERSONAL DATA IN MARKETING PROCESSES570
- I.PROCESSING OF PERSONAL DATA IN MARKETING PROCESSES IN THE LIGHT OF THE DECISIONS OF THE BOARD570
- II.SUMMARY OF THE SUBJECT IN OUTLINE577
- § 14.ARTIFICIAL INTELLIGENCE TECHNOLOGIES AND DATA PROTECTION LAW579
- I.CONCEPTS RELATING TO THE SUBJECT579
- II.ARTIFICIAL INTELLIGENCE AND THE PROCESSING OF PERSONAL DATA582
- III.DATA PROCESSING BY ARTIFICIAL INTELLIGENCE UNDER PERSONAL DATA PROTECTION LAW583
- IV.AUDIO, VISUAL OR WRITTEN MESSAGES GENERATED BY ARTIFICIAL INTELLIGENCE588
- § 15.PROCESSING OF PERSONAL DATA IN THE LEGAL PROFESSION: CONTROVERSIAL POINTS IN THE LIGHT OF THE DECISIONS OF THE BOARD591
- I.IN GENERAL591
- II.PROCESSING OF PERSONAL DATA IN THE COURSE OF PRACTISING THE LEGAL PROFESSION591
- A.The Debate on Whether Lawyers Are Controllers or Processors591
- B.Can Lawyers’ Professional Activities Be Regarded as Falling within the Exception Laid Down in Art. 28(1)(d) of the Law on the Protection of Personal Data (KVKK)?594
- C.The Obligation to Inform and the Obligation of Secrecy596
- D.Inclusion of Personal Data in Pleadings Submitted to the Case File by Lawyers597
- E.Sending of Garnishee Notices to Relatives of the Debtor598
Chapter FivePROTECTION OF PERSONAL DATA IN TURKISH CRIMINAL LAW AND THE LAW OF MISDEMEANOURS86 headings
- § 16.PROTECTION OF PERSONAL DATA THROUGH CRIMINAL AND MISDEMEANOUR NORMS601
- I.IN GENERAL601
- II.THE NEED TO PROTECT PERSONAL DATA THROUGH CRIMINAL AND MISDEMEANOUR NORMS601
- III.PROTECTION OF PERSONAL DATA IN THE TURKISH CRIMINAL CODE (TCK) AND THE KVKK603
- § 17.OFFENCES AIMED AT PROTECTING PERSONAL DATA IN THE TURKISH CRIMINAL CODE604
- I.THE OFFENCE OF RECORDING PERSONAL DATA (ART. 135)604
- A.In General604
- B.Legal Interest Protected by the Offence605
- C.Conformity with the Statutory Definition of the Offence (Tatbestandsmäßigkeit)609
- 1.Material (Objective) Elements of the Statutory Definition609
- a.Perpetrator609
- b.Victim610
- c.Subject Matter of the Offence611
- d.Conduct (Act)614
- e.Result615
- f.Aggravated (Qualified) Forms of the Offence616
- i.Where Special Categories of Personal Data Constitute the Subject Matter of the Offence (TCK Art. 135(2))616
- ii.Aggravated Forms Arising from the Status of the Perpetrator (TCK Art. 137(1))617
- 2.Mental (Subjective) Element of the Statutory Definition618
- D.The Element of Unlawfulness619
- 1.Meaning of the Expression “Unlawfully” in the Definition of the Offence619
- a.Our View on Expressions of This Kind from the Standpoint of the Theory of the Offence619
- b.Our View on These Expressions in Arts 135 and 136 of the TCK621
- 2.Consent of the Victim624
- a.The Time at Which and the Form in Which Consent Must Be Present626
- b.Where the Personal Data Have Been Made Public by the Data Subject627
- c.Cases in Which Explicit Consent Is Not Required for the Processing of Personal Data under Law No. 6698 (KVKK)634
- d.Cases in Which Explicit Consent Is Not Required for the Processing of Special Categories of Personal Data under Law No. 6698 (KVKK)635
- 3.Reliance on Authority Conferred by Law636
- a.Application of the Measure of Search and Seizure in Information Systems under the Code of Criminal Procedure (CMK)636
- b.Processing of Personal Data within the Scope of the State’s Intelligence Activities637
- c.Evaluation of Signal Information under Article 135 of the CMK639
- d.Processing of Health Data as a Special Category of Personal Data644
- 4.The Problem of Recording Information on Persons’ Political, Philosophical or Religious Views and Racial Origins645
- 5.The Problem of the Fate of Personal Data in Information Systems Provided to Employees in the Public and Private Sectors646
- 6.Breach of the Obligations under the KVKK Does Not in Itself Constitute an Offence646
- E.Special Forms of Appearance of the Offence647
- 1.Attempt647
- 2.Participation648
- 3.Concurrence648
- F.Sanction, Investigation and Prosecution652
- II.THE OFFENCE OF GIVING OR OBTAINING PERSONAL DATA (ART. 136)652
- A.In General652
- B.Legal Interest Protected by the Offence652
- C.Conformity with the Statutory Definition of the Offence (Tatbestandsmäßigkeit)653
- 1.Material (Objective) Elements of the Statutory Definition653
- a.Perpetrator653
- b.Victim653
- c.Subject Matter of the Offence654
- d.Conduct (Act)655
- i.Giving Personal Data to Another Person661
- ii.Dissemination of Personal Data663
- iii.Obtaining Personal Data664
- e.Result665
- 2.Mental (Subjective) Element of the Statutory Definition666
- 3.Aggravated (Qualified) Forms of the Offence671
- D.The Element of Unlawfulness673
- E.Special Forms of Appearance of the Offence675
- 1.Attempt675
- 2.Participation676
- 3.Concurrence676
- F.Sanction, Investigation and Prosecution681
- III.THE OFFENCE OF FAILURE TO DESTROY PERSONAL DATA (ART. 138)681
- A.In General681
- B.Legal Interest Protected by the Offence681
- C.Conformity with the Statutory Definition of the Offence (Tatbestandsmäßigkeit)682
- 1.Material (Objective) Elements of the Offence682
- a.Perpetrator682
- b.Victim684
- c.Subject Matter of the Offence685
- d.Conduct (Act)685
- i.The Perpetrator Being Charged with the Duty and Allowing the Time Limit to Expire685
- ii.Failure to Destroy the Data686
- e.Aggravated (Qualified) Form of the Offence687
- 2.Mental (Subjective) Element of the Offence689
- D.The Element of Unlawfulness689
- E.Special Forms of Appearance of the Offence690
- 1.Attempt690
- 2.Participation690
- 3.Concurrence690
- F.Sanction, Investigation and Prosecution691
- IV.THE OFFENCE OF FAILURE TO ERASE OR ANONYMISE PERSONAL DATA PROVIDED FOR IN ART. 17(2) OF LAW NO. 6698 (KVKK)692
- § 18.ADMINISTRATIVE SANCTIONS AIMED AT PROTECTING PERSONAL DATA PROVIDED FOR IN THE KVKK693
- I.IN GENERAL693
- II.ADMINISTRATIVE SANCTIONS PROVIDED FOR IN THE KVKK694
- § 19.OUR ASSESSMENTS AND VIEWS ON THE PROTECTION OF PERSONAL DATA THROUGH CRIMINAL AND MISDEMEANOUR NORMS696
Chapter SixTHE PROCESS OF COMPLIANCE WITH PERSONAL DATA PROTECTION LEGISLATION23 headings
- § 20.THE PROCESS OF COMPLIANCE WITH PERSONAL DATA PROTECTION LEGISLATION701
- I.IN GENERAL701
- II.THE NEED FOR COMPLIANCE PROCESSES AND THE STATUTORY BASIS702
- III.THE COMPLIANCE PROCESS707
- A.Establishment and Implementation of the Compliance Strategy707
- B.Kick-off Meeting707
- C.Drawing up the Personal Data Inventory707
- D.Gap Analysis710
- E.Compliance Consultancy711
- 1.Preparation of the KVKK Policy711
- 2.Data Protection Officer/Committee711
- 3.Finalisation of the Inventory and Registration with VERBİS715
- 4.Explicit Consent Arrangements716
- 5.Matters Relating to the Obligation to Inform716
- 6.Data Protection Undertakings and Updating of Contracts717
- 7.Transfer Abroad718
- 8.Carrying out Data Minimisation and Disposal Operations719
- 9.Determination of the Security Measures to Be Taken720
- 10.Preparation and Updating of KVKK Policies and Procedures720
- F.Data Protection Consultancy after the Completion of the Compliance Process727
- IV.DATA PROTECTION TRAINING AND AWARENESS-RAISING728
- V.REVIEW731
- VI.ASSESSMENT AND OUR VIEW732
- Bibliography735
- Index749
Related publications
Dülger, Murat Volkan, Legislation on Information Technology, Personal Data Protection and Internet Communication (Bilişim, Kişisel Verilerin Korunması ve İnternet İletişimi Mevzuatı), 7th ed., Seçkin Publishing, Ankara, 2021.
Dülger, Murat Volkan, “The Use of Bulk Data and Metadata in Preventive Policing and Intelligence Work from the Standpoint of Human Rights, Personal Data Protection and Criminal Procedure Law” (İnsan Hakları, Kişisel Verilerin Korunması ve Ceza Muhakemesi Hukuku Açısından Önleyici Kolluk Hizmetleri ve İstihbari Çalışmalarda Toplu Veri ve Metadata Kullanımı), conference presentation, 2026.
Dülger, Murat Volkan, “Lawyers' Obligations under the KVKK in the Light of the Board's Decisions” (Kurul Kararları Işığında Avukatların KVKK Yükümlülükleri), conference presentation, 2025.
Dülger, Murat Volkan / Gümüş, Gülçin, “The Right to Be Forgotten”, Essays in Honour of Prof. Dr. Yadigar İzmirli (Prof. Dr. Yadigar İzmirli'ye Armağan), 2024.
Dülger, Murat Volkan / Gümüş, Gülçin, “Assessment of the Amendments to the KVK Law on the Processing of Special Categories of Personal Data and the Transfer of Data Abroad” (KVK Kanunu’nda Özel Nitelikli Kişisel Verilerin İşlenmesi ve Yurt Dışına Veri Aktarımı Kapsamında Yapılan Değişikliklere İlişkin Değerlendirmeler), Academia.edu, 25 March 2024.